This article is a beginner’s guide on how to set up DMARC because, really, DMARC sounds more technically intimidating than it actually is.
In this guide I’m going to cover the entire DMARC setup process, which includes:
- Making sure you have SPF/DKIM in place
- Creating your DMARC policy
- Adding the record to your domain
- Testing to make sure everything worked
That process should take about five minutes or less. The only reason I didn’t want to call this a “5-minute guide” is because you’ll also need SPF or DKIM in place before you can set up DMARC. If you need to set up one of those and then DMARC, that will take slightly longer.
November 9, 2026 update: Resolved Sending to Outlook.com or Hotmail? In early November 2026, senders have reported a new rejection from Microsoft email clients for messages from domains without DMARC — including low-volume senders. While it’s now been resolved, we still recommend reading about the Outlook issue and what to do.
How to Set Up DMARC: Table of Contents
- What Is DMARC in Under 100 Words?
- Step 1: Testing Whether SPF/DKIM Are Set Up for Your Domain
- Step 2: Create Your DMARC Record
- Step 3: Adding Your DMARC Policy Record to Your Domain
- Outlook Is Rejecting Some Emails Without DMARC [Nov 2026 update]
- How to Set Up DMARC: Next Steps
What Is DMARC in Under 100 Words?
Domain-based Message Authentication, Reporting & Conformance (DMARC) helps receiving servers check whether a message is authorized to use the domain in its visible From address.
A message passes DMARC when SPF or DKIM passes and the authenticated domain aligns with the From domain. Your DMARC policy tells receivers what action you request when neither passes with alignment.
You publish that policy as a DNS TXT record. DMARC can help protect against spoofing and meet receiving providers’ authentication requirements, but it does not guarantee inbox placement.
How do SPF and DKIM relate to DMARC?
SPF stands for Sender Policy Framework. It’s a domain record where you specify what mail servers have permission to send emails using your domain.
DKIM stands for DomainKeys Identified Mail. It’s like a digital signature that’s attached to your emails to help a mail server determine whether the email was authorized.
While SPF, DKIM, and DMARC are referred to as the three main authentication methods for email, DMARC works differently than the other two.
DMARC relies on SPF and DKIM, plus domain alignment. An SPF or DKIM pass for an unrelated domain is not enough. At least one must pass with a domain that aligns with the domain in the visible From address. With the usual relaxed alignment, domains can align when they share the same organizational domain. See Microsoft’s explanation of DMARC and alignment.
Do I need to set up DMARC?
“Need” is a strong word… but you really should set up DMARC.
If you send email from a domain you control, you should set up DMARC — even if you are not a bulk sender.
Google and Yahoo/AOL’s bulk sender requirements that went into place back in 2024 already make DMARC necessary for many senders. (Our guide to Google and Yahoo’s sender requirements explains those rules.)
- All senders are required to have a SPF or DKIM recordin place; DMARC is not required.
- However, if you’re setting up SPF/DKIM, there’s no reason not to also set up DMARC.
- Bulk senders — defined as people sending 5,000+ messages in a day to gmail.com addresses or a large volume of daily emails to Yahoo/AOL addresses — are required to have SPF, DKIM, and DMARC set up.
But just because you’re sending low volumes, that still doesn’t make DMARC optional. (For instance, check out the November 2026 Outlook rejections section of this article.)
If you already have DMARC, check that it is valid and that your actual outgoing messages pass authentication. You do not need to add another record.
Does DMARC help my deliverability?
Yes. DMARC, along with the other email authentication methods, can help with deliverability.
None of them is a magic bullet, though. If you set up a DMARC policy, that doesn’t mean suddenly every single email you send will go to the inbox and not the spam folder.
DMARC is one helpful deliverability tool you have at your disposal, but many other factors also contribute to where your emails land. (For instance, things like your domain and IP reputation, the content of your messages, and how many people have marked your prior emails as spam.)
Do I need to set up DMARC if I have a gmail.com email address?
You do not need to set up DMARC for your gmail.com address… because you can’t.
In order to set up DMARC, you need to be able to access your domain name’s DNS records. You don’t have access to gmail.com’s records, since Google owns that domain name. And they already have SPF, DKIM, and DMARC set up.
What if I don’t control my own domain name?
You might not be able to access the DNS records for your domain name. (Example: Maybe you work for a company and send emails through them.)
In that case, if you don’t have a DMARC policy in place, you’ll need to talk to someone to have them set that up. That might be an IT person or another administrator; really, whoever’s in charge of the domain.
Now let’s cover how to set up DMARC.
Step 1: Testing Whether SPF/DKIM Are Set Up for Your Domain
Publishing a DMARC record is only part of the setup. Your outgoing messages also need to pass SPF or DKIM with alignment to your From domain to pass DMARC. Configure both SPF and DKIM where your sending service supports them; some receiving providers require both for bulk senders.
That means our first step is going to be determining whether or not you already have SPF/DKIM in place — and if not, setting up one of them.
GMass has a free email analyzer tool where you can check out whether you have SPF and DKIM records for your domain. (And while we’re in there, we’ll also check if you have DMARC set up already too.)
Head over to the email analyzer, then copy the test address it provides.
Go to your email account and send an email to that address using the same From address and sending service as your campaigns. If your campaign uses an SMTP service, test through that service too; a normal Gmail send may use a different authentication setup.
It should only take a few seconds for GMass to process your email and show you everything going on behind-the-scenes with your sending process.
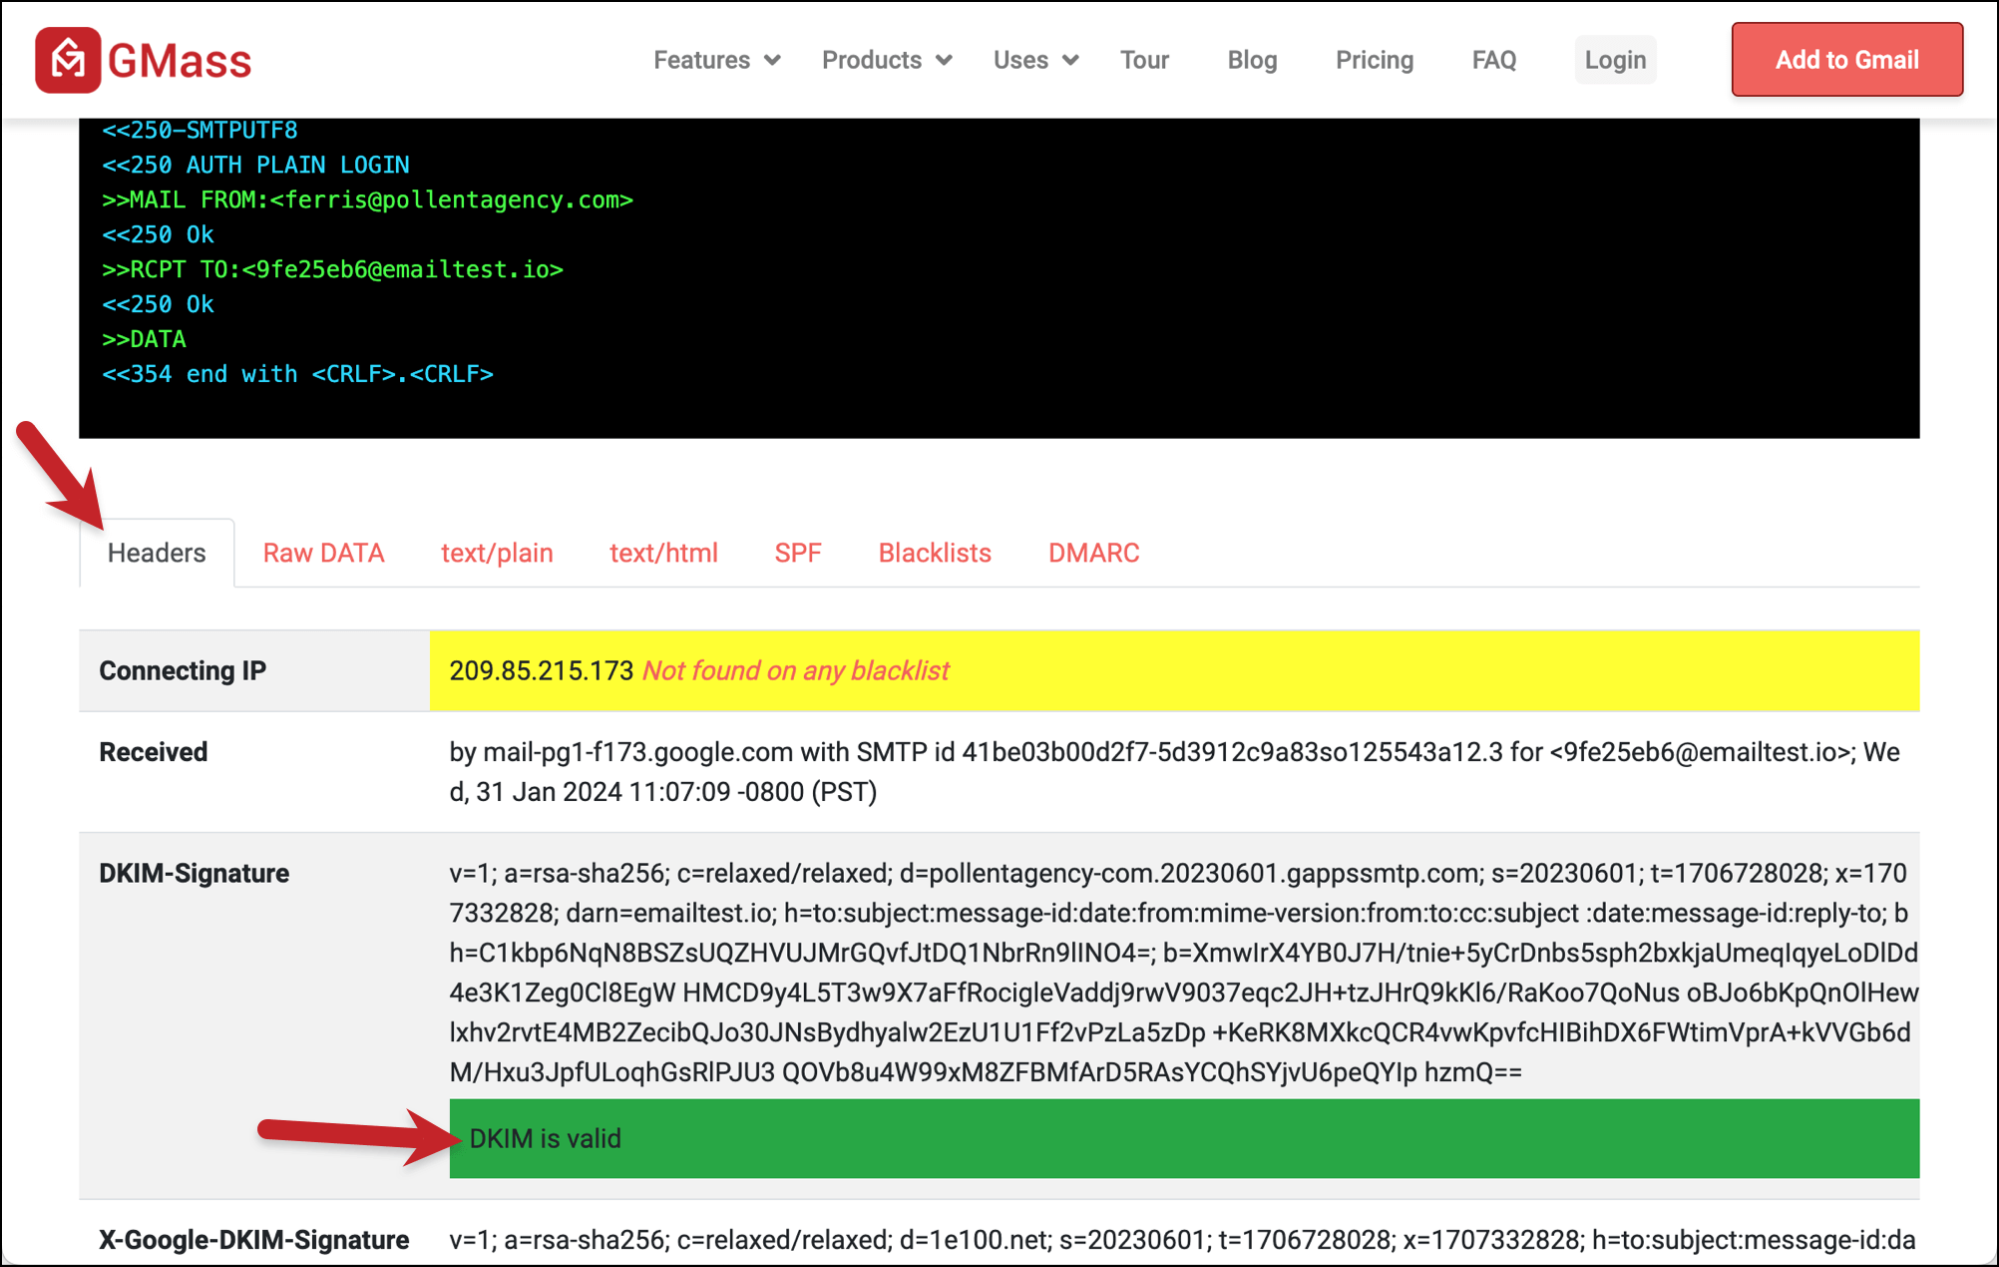
You can see whether you have a valid DKIM signature in the Headers section…
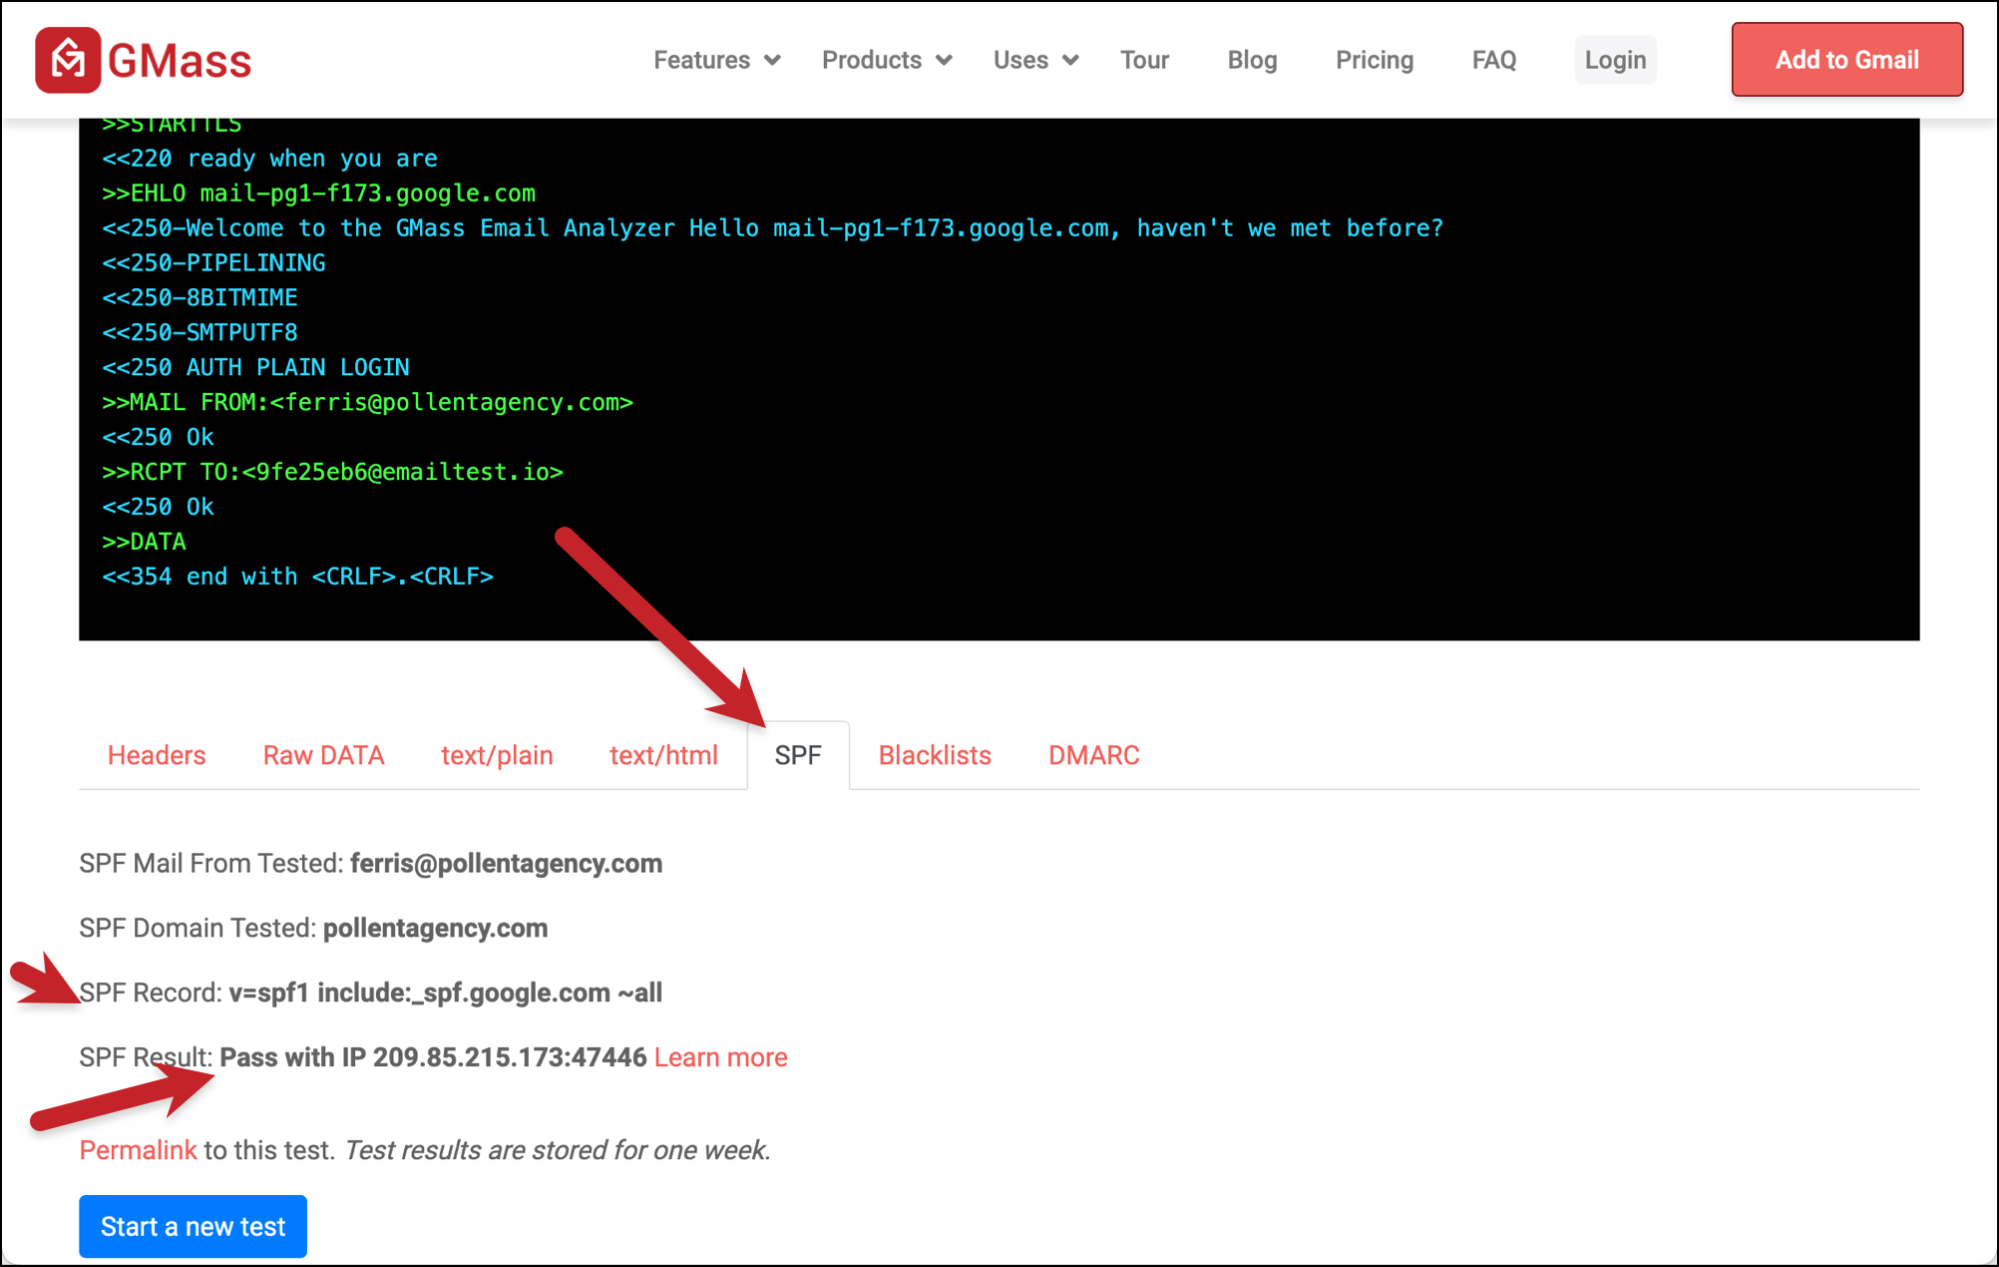
If you have an SPF record, that will be in the SPF section…
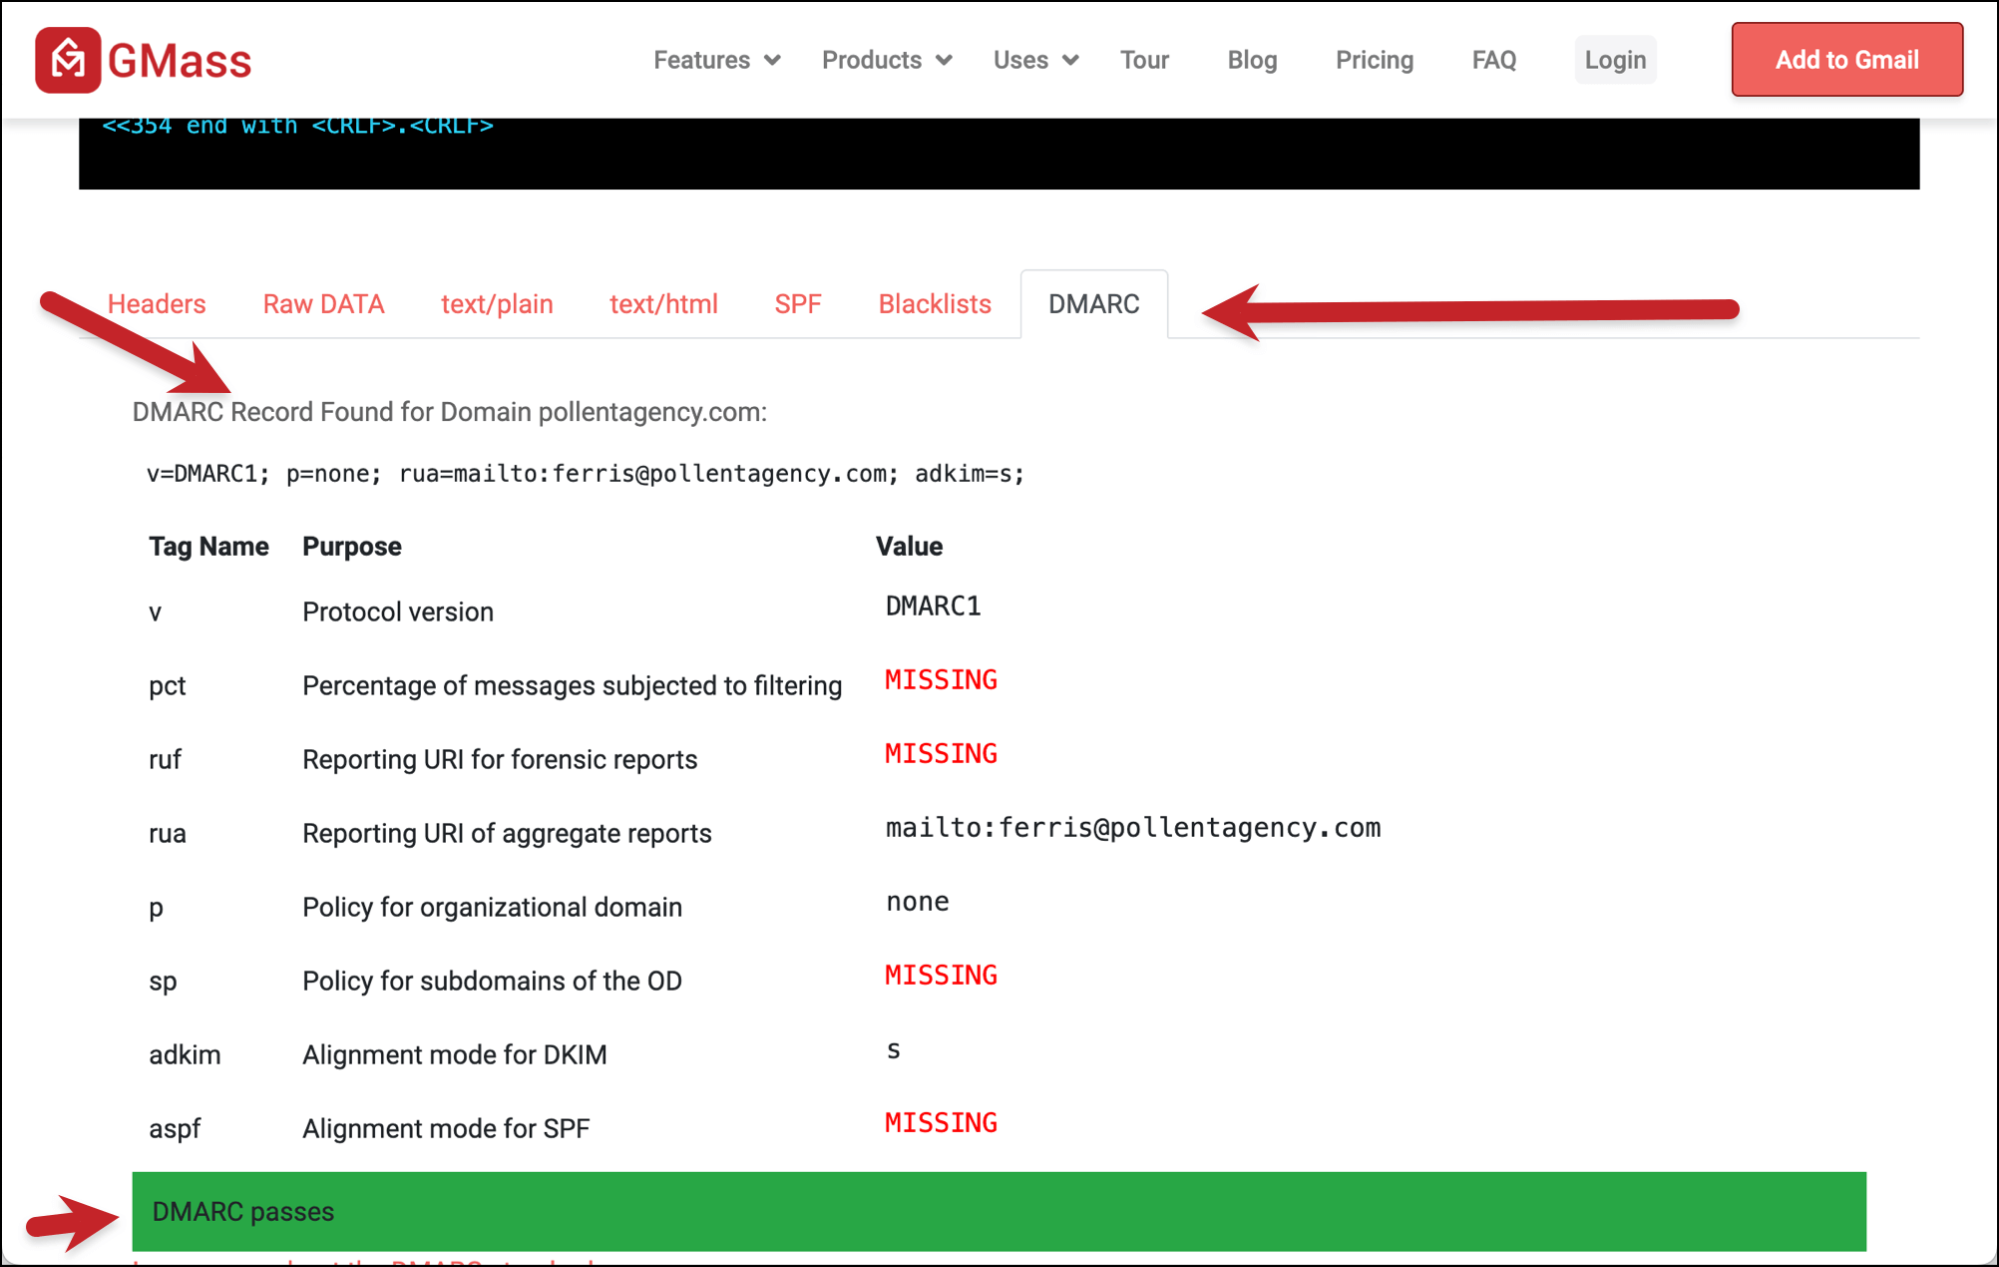
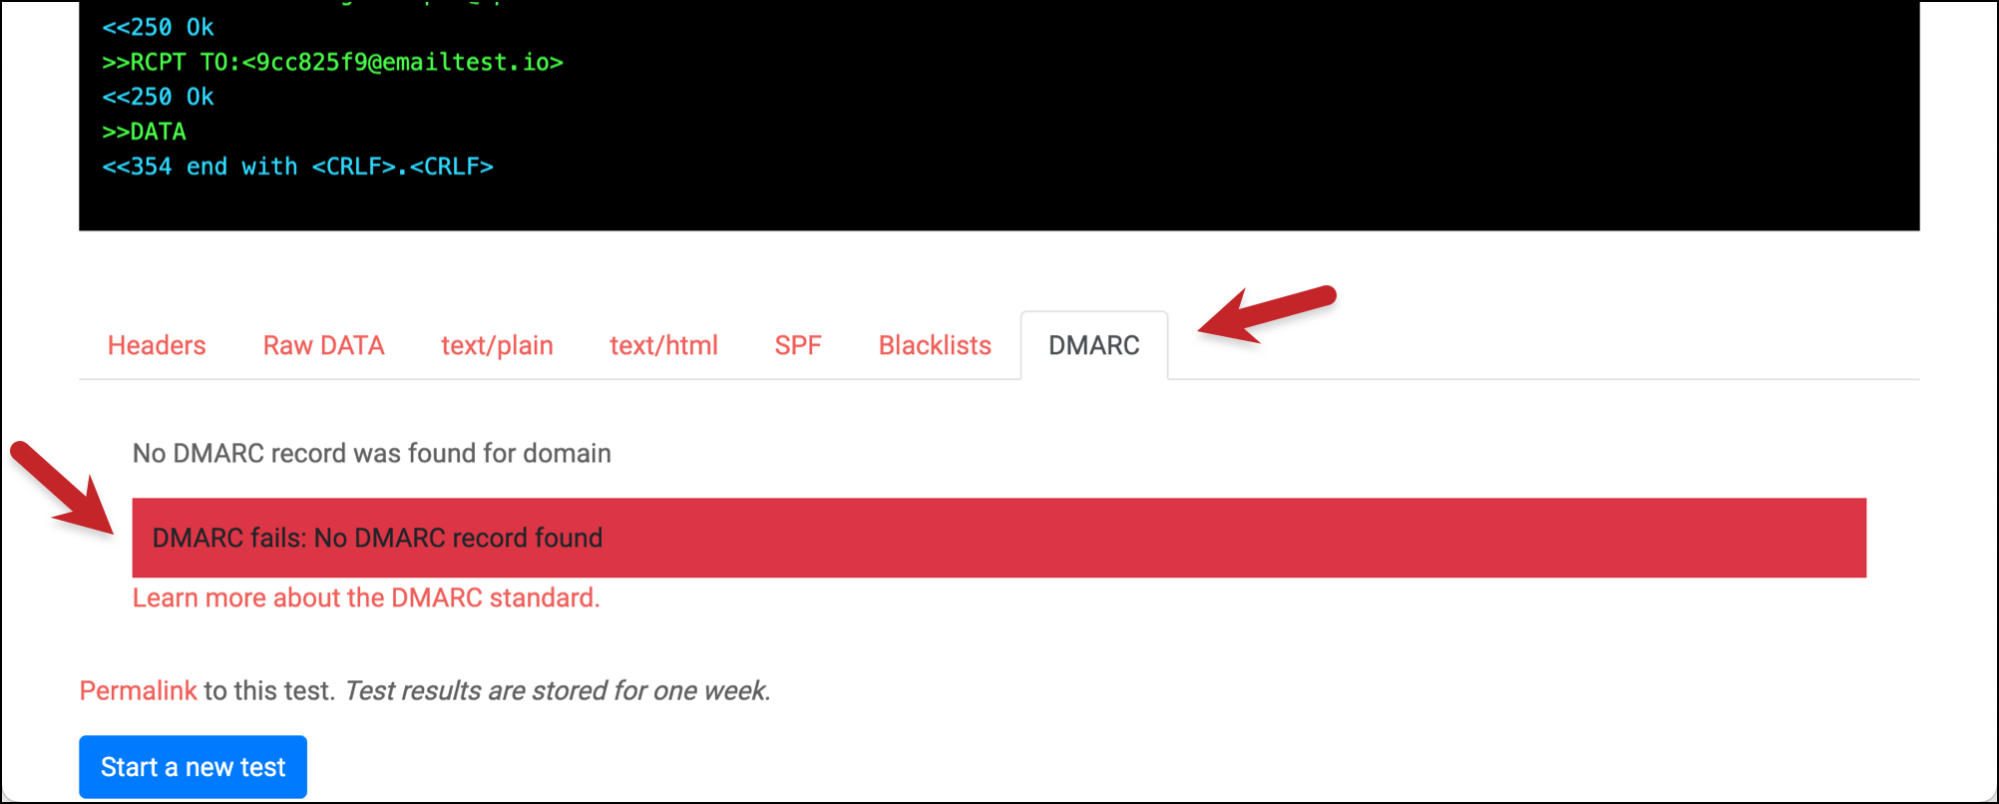
And you can see if you have a DMARC record in place in the DMARC section…
…or not.
Why do I have a DKIM record in place when I know I’ve never set one up?
If you have a DKIM record in place and you know you’ve never gone through this process, it’s likely the default DKIM record Google uses for Google Workspace accounts.
You should still set up your own so you can achieve DKIM alignment with DMARC.
Setting up SPF or DKIM for your domain
We’ve published quick guides on adding SPF and DKIM records for your domain.
Either one will take about five minutes, assuming you have access to your domain’s DNS records at your registrar or host.
- Here’s the guide to set up SPF
- And here’s how to set up DKIM
If you’re choosing one or the other, we recommend DKIM because it’s easier to pass DMARC alignment with DKIM. However, it’s really best to set up both where possible.
We explain why in our article on using GMass’s special DKIM settings (which you’d use if you were sending emails in GMass using a SMTP service, otherwise don’t worry about it).
Once you have your SPF or DKIM policy in place, you’re ready to set up DMARC.
Step 2: Create Your DMARC Record
First, check for an existing record. If your domain already has DMARC, review that record instead of adding a second one. Keep an existing stricter policy unless your domain administrator determines that it needs to change.
For a domain without DMARC, this is a minimal starter record:
v=DMARC1; p=none;Publish it as a TXT record at _dmarc.example.com, replacing example.com with your domain. Most DNS providers let you enter just _dmarc in the Name or Host field.
p=none means you are not asking receivers to quarantine or reject messages because they fail DMARC. It does not disable the receiver’s other filtering, guarantee delivery, or provide full protection against domain spoofing.
To receive aggregate reports, add a rua address that you control, for example:
v=DMARC1; p=none; rua=mailto:dmarc@example.com;Replace that example address with a real reporting mailbox or the address supplied by your DMARC monitoring service. The minimal record without rua does not request emailed reports. Google’s DMARC setup guide explains reporting and the DNS setup process.
If you’d prefer help generating a record, use the wizard below.
A DMARC policy is usually just one line of text — a line you do not have to write yourself.
I use a site called the DMARC Record Wizard to create my DMARC records. There are plenty of other DMARC generators out there if you just have to do something different.
Our recommended settings:
- For the type of DMARC policy, select the “nothing yet, just collect data” option.
- For the reporting email address, enter a dedicated mailbox you control or the address provided by your DMARC monitoring service.
- You do not want to receive individual failure reports.
- We recommend relaxed alignment for both DKIM and SPF.
- For subdomains, you can leave a separate subdomain policy unset. Subdomains without their own DMARC record generally inherit the parent domain’s policy; this does not exclude them from DMARC.
- Apply to 100 percent of email.
The tool should spit out a result that looks quite a bit like this:
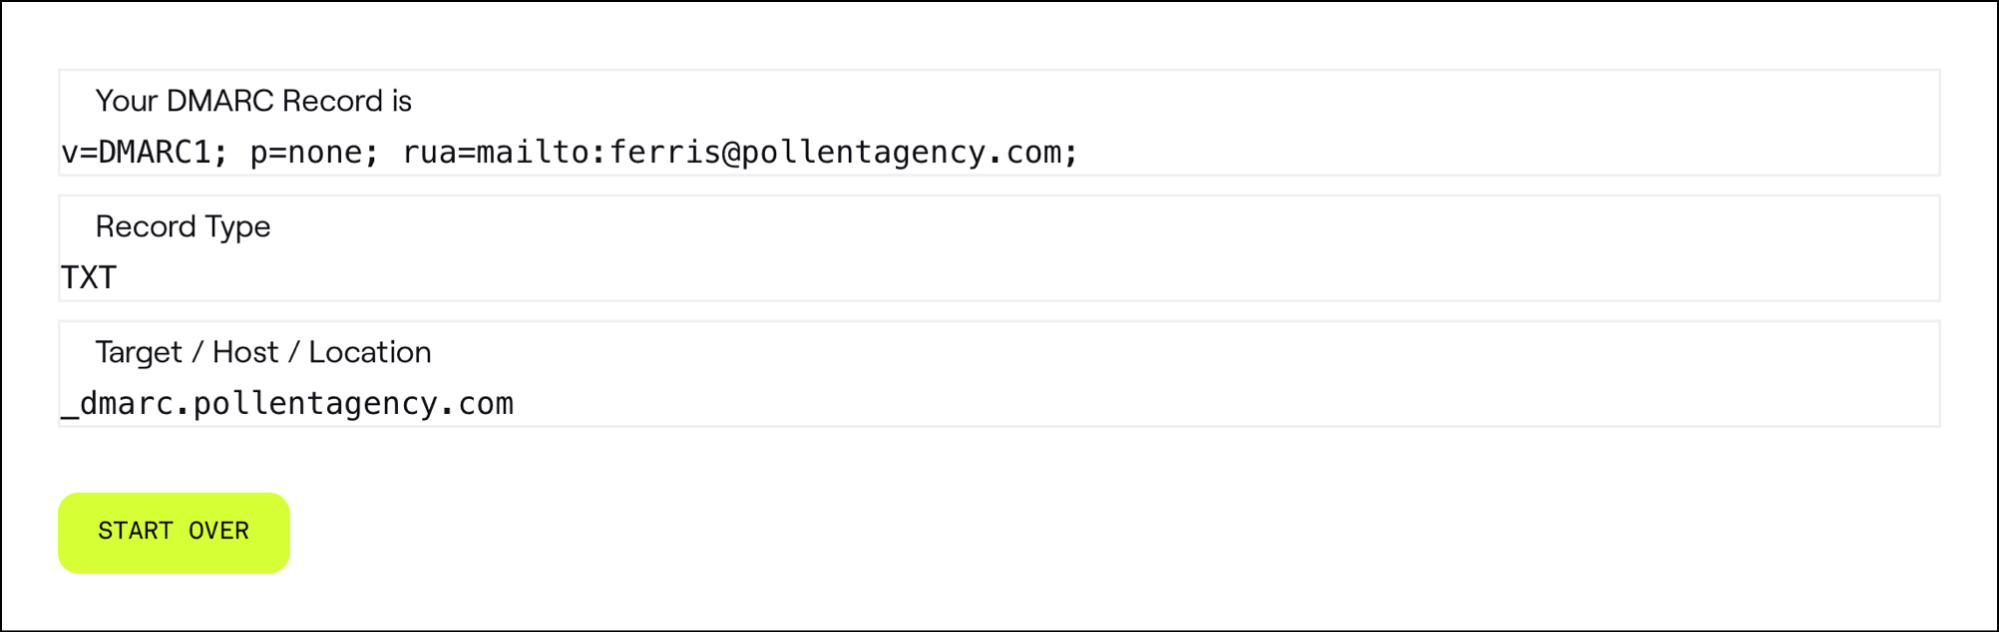
That’s all you need; you’re now ready to set up the policy for your domain.
Step 3: Adding Your DMARC Policy Record to Your Domain
In order to set up your DMARC policy for your domain, you’ll need to be able to add a Domain Name System (DNS) record.
Since you’re a beginner, it’s most likely that you’ll edit your DNS records at your domain registrar (e.g., GoDaddy, Namecheap, and the rest).
If you log into your account at your registrar, attempt to edit the DNS records for your domain, and they tell you the records are managed elsewhere, it could be your web hosting company. (There are also third-party DNS management platforms, but it’s much less likely you’re using one of those.)
For this example, I’m going to show you how to create your DMARC record at your domain registrar.
How to create your DMARC record at your domain registrar
I’ll demonstrate how to create the record at GoDaddy. If you’re using a different registrar, it won’t look exactly like this but the basics are the same: Go to your domain, find the section with its DNS settings, add a record.
First, log into your domain registrar, then go to your domain.
Go to the DNS management options for the domain, then find the link or button to add a new record.
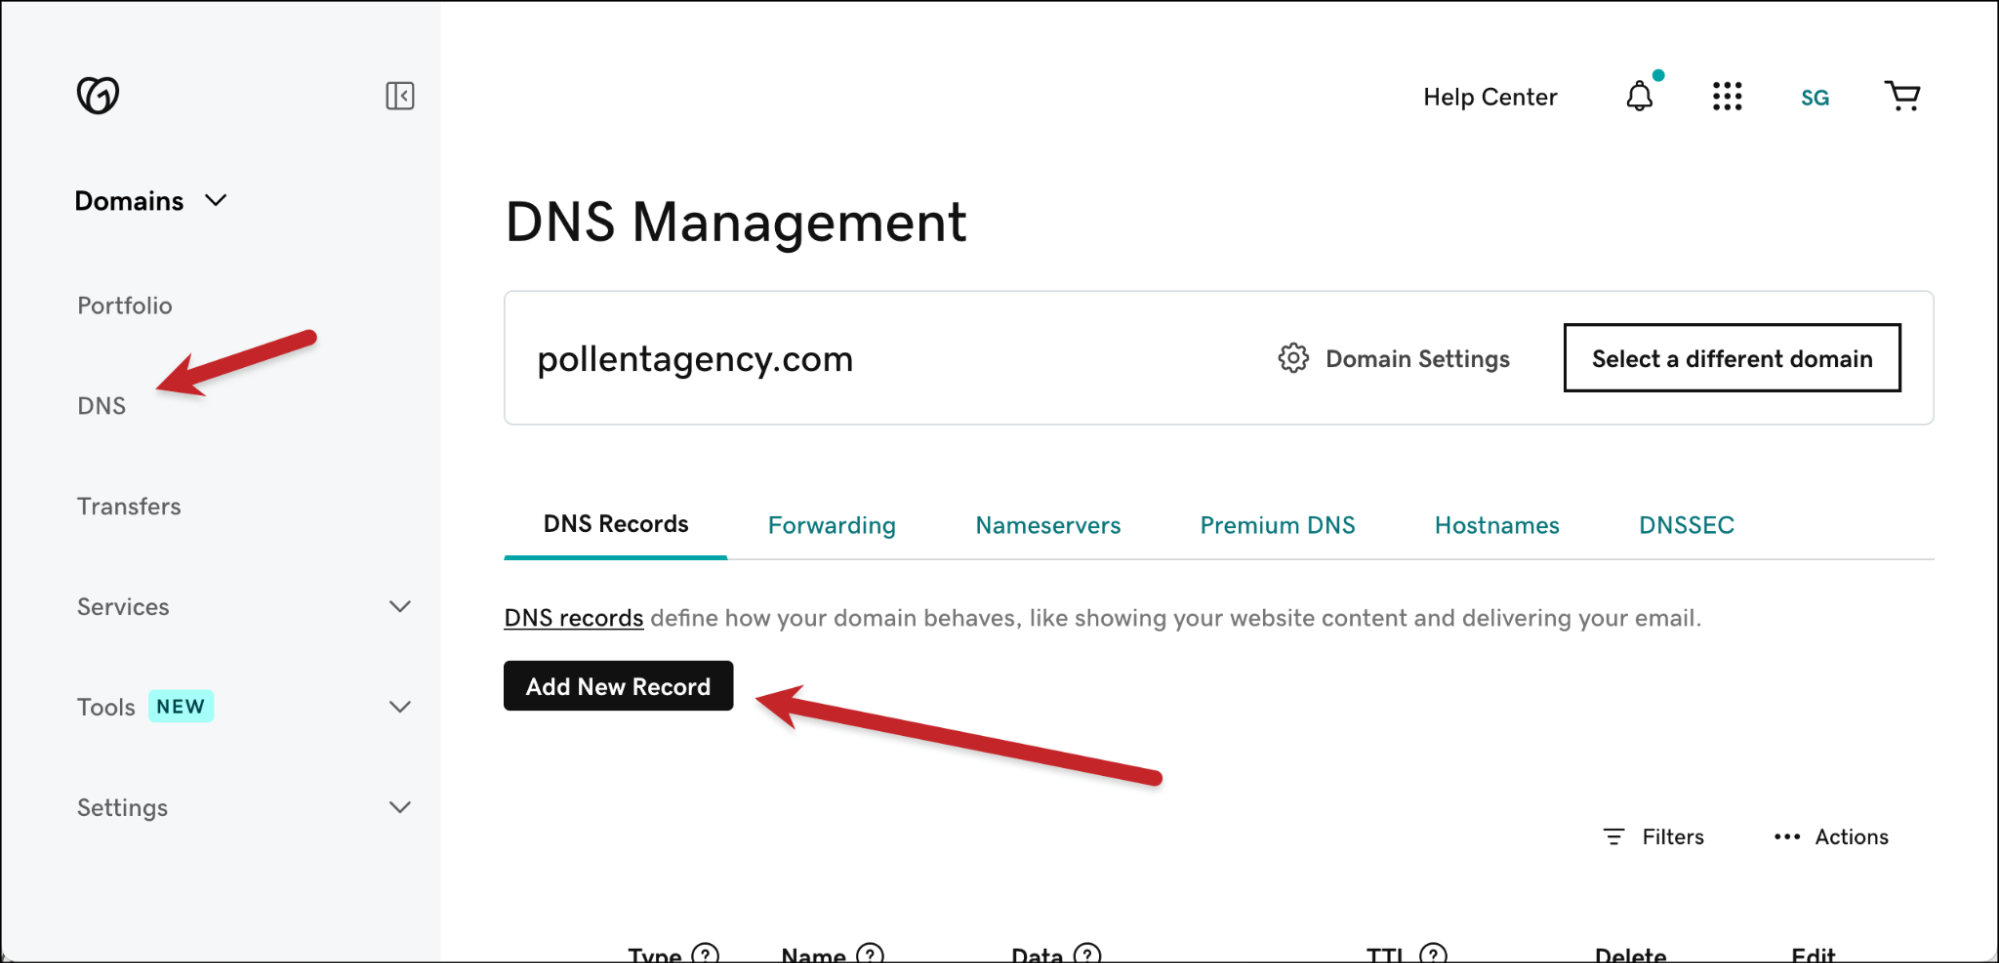
Now enter these settings:
- Type: TXT
- Name/Host: Usually
_dmarc. If your provider requires the full hostname, use_dmarc.example.comwith your own domain. Check whether it appends your domain automatically so you don’t enter the domain twice. - Value: Your DMARC record, such as
v=DMARC1; p=none;, or the full record generated by the wizard with your reporting address. - Time-to-Live (TTL): 1 hour or 3600 seconds
Then save the record.
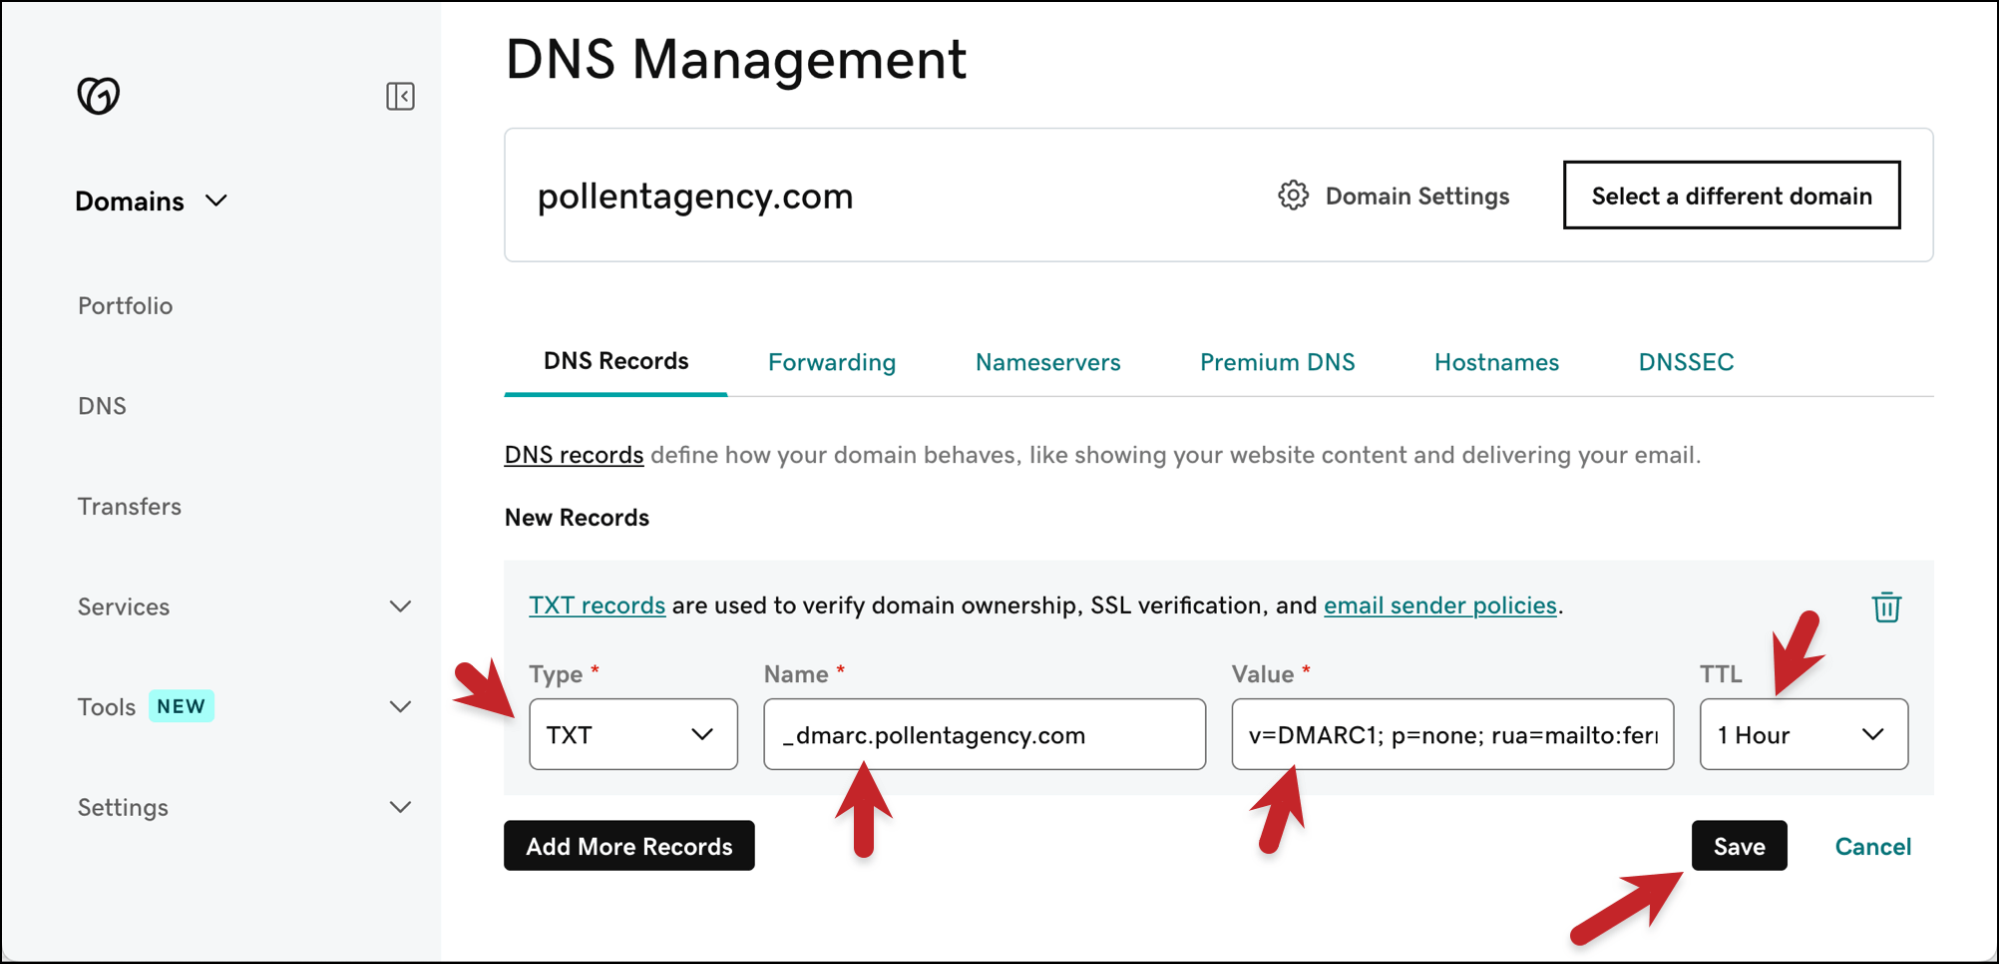
Now when you scroll through the list of DNS records for your domain, you should see your new TXT record.
It will take up to 48 hours for the DNS changes to propagate. It usually doesn’t take that long — in my experience, usually everything is set in a few hours.
After you’ve waited at least a few hours, you can run the GMass email analyzer again to check if your new DMARC record is now up and valid.
Outlook May Reject Some Emails Without DMARC [Nov 2026 update]
If you send from your own domain, check your DMARC setup even if you only send a few emails a day.
In early November 2026, MailRoute reported that it began seeing rejections the day before from Microsoft’s consumer email services, including Outlook.com, Hotmail, Live.com, and MSN.com. Affected messages included mail from low-volume senders with working SPF and DKIM but no DMARC record.
This confirmed something similar we’d started noticing at GMass.
The rejection looks like this:
550 5.7.1 Message rejected: Message lacks SPF/DKIM/DMARC Auth Records (AS9031519)You may also see it inside a longer failure notice headed 550 5.7.23 or “SPF validation error.” Read the full diagnostic, not just the heading. Senders reported that combination on Microsoft’s support forum.
This is separate from Microsoft’s published 2025 requirements for high-volume senders, which describe the 550 5.7.515 authentication rejection. The November issue has been observed beyond bulk sending. These reports concern Microsoft’s consumer mail service; they do not establish a new universal rule for every Microsoft 365 business mailbox.
This has since been resolved and is no longer happening. However, it’s still highly, highly recommended for senders to set up DMARC to avoid situations like this in the future.
What should you do if Outlook rejects your email?
- Check the domain in your From address. If you send as
you@example.com, check DMARC forexample.com. If you send from a subdomain, also check whether it inherits a DMARC policy from its parent domain. - If DMARC is missing, publish a starter record. Add a TXT record named
_dmarcwith the valuev=DMARC1; p=none;. The record creation and DNS setup sections below walk you through it. - If DMARC already exists, investigate before changing it. Don’t add a duplicate record or replace an existing
p=quarantineorp=rejectpolicy withp=none. Check that the record is valid and your sending service passes SPF or DKIM with alignment to your From domain. - Test after your DNS update is visible. Use the same From address and sending service as your campaign, then send a small test to an Outlook.com or Hotmail address before retrying affected recipients.
In tests published November 8, DMARKOFF reproduced the rejection and found that publishing DMARC, including with p=none, resolved it for the tested domains. That is evidence for fixing a missing record, not a guarantee that every authentication rejection will disappear or that messages will land in the inbox.
For GMass users: GMass recognizes the “Message lacks SPF/DKIM/DMARC” rejection as a block, unless you have enabled “Treat blocks as bounces.” This rejection does not, by itself, mean the recipient’s address is invalid. Classifying it correctly does not fix the sender’s authentication setup or automatically retry the message.
How to Set Up DMARC: Next Steps
Once your record is published and your test messages pass, you have set up DMARC for your sending domain.
DMARC helps you meet authentication requirements and address missing-record rejections like the November 2026 Outlook issue. It is still only one part of deliverability.
If you started with p=none, add reporting, review your legitimate sending sources, and work toward p=quarantine or p=reject once those sources authenticate correctly. Microsoft’s setup guide describes a gradual rollout. Don’t switch to an enforcement policy without checking the services that send mail using your domain.
And because I know you’re hot on deliverability…
If you’re not a GMass user yet, 99% of GMass users report the best deliverability they’ve ever had.
GMass has an entire suite of deliverability tools, including the unique Spam Solver, to help make sure your messages get to your prospects and don’t wind up in their spam folders.
You can get started with a free trial of GMass by downloading the Chrome extension — there’s no credit card required.
GMass works right inside of Gmail, which makes it easy to use (there’s no new software platform to learn) and you can test it out by sending up to 50 emails per day during your free trial.